
Encryption is considered one of the https://ishanmishra.in/reasons-why-selling-your-infants-items-online-is-a-risk/ most effective safeguards for protecting delicate info, yet it is only as strong as its implementation. Organizations rely on encryption to safe buyer data, monetary transactions, cloud workloads, and confidential enterprise communications. Nevertheless, weak cryptographic practices, poor key administration, outdated algorithms, and implementation errors can create cryptography failures that expose important data to cybercriminals. In today’s digital landscape, cryptographic methods are important for shielding delicate information and making certain secure communications. However, even the most strong encryption options can be compromised via cryptographic failures. For C-level executives, understanding these dangers is vital—not solely to safeguard information but additionally to protect the organisation’s reputation and long-term viability.
Frequent Causes Of Cryptography Failure
Users or developers with inadequate information of cryptographic greatest practices may by chance misconfigure encryption settings or fall victim to phishing or other social engineering tactics. Superior attackers analyze physical or operational traits, such as energy consumption, timing, or electromagnetic emissions, to deduce cryptographic keys with out directly breaking the algorithm. A cryptographic failure, subsequently, is not simply a technical glitch; it represents a extreme breakdown within the processes meant to protect data. Encrypting knowledge each throughout transmission over networks and whereas stored is crucial to ensure data integrity and privateness. SHA-1, once a widely used cryptographic hash function, was officially deemed insecure after researchers demonstrated a practical collision attack. Participation in information-sharing platforms and collaboration with industry peers may help organizations acquire insights into frequent challenges and mitigation methods.
Sha-1 Deprecation And Collision Assault (
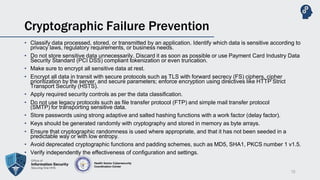
By investing in sturdy cryptographic practices, updating protocols, coaching staff, and developing a resilient incident response plan, organisations can considerably scale back their risk of cryptographic failures. Given the complex and evolving threat panorama, a proactive and strategic strategy to cryptographic safety is important for sustaining the trust of consumers, companions, and traders alike. Stopping cryptography failure requires more than implementing encryption it demands strong governance, safe key administration, and continuous monitoring. Organizations should adopt a layered approach that protects delicate information throughout its lifecycle.
- By simulating real-world cyber assaults, penetration testers can uncover weaknesses in an application’s security posture, including cryptographic failures.
- Keep Away From hardcoding keys, reusing the same key a quantity of occasions, or using easily predictable keys.
- One of essentially the most notorious cryptographic failures, Heartbleed was a vulnerability in OpenSSL, a broadly used cryptographic library.
- For many organizations, defending knowledge at rest is a a lot more durable problem and its failures usually end in devastating knowledge breaches and loss.
- Cryptography is the science of securing data and communications by encoding information in order that solely authorised events can access it.
Insider Threats And Cryptographic Failures
Cryptography includes the use of algorithms and mathematical principles to encode info, ensuring that solely licensed parties can access or perceive the information. TrueCrypt, a well-liked open-source encryption tool, was abruptly discontinued following revelations of potential vulnerabilities.
The attack triggered hundreds of tens of millions of dollars in damages and severely disrupted critical infrastructure, notably inside the UK’s National Health Service (NHS). The GDPR is the European Union’s complete information protection law, designed to ensure that private data is dealt with securely and transparently. In 2020, a cloud service supplier inadvertently revealed its non-public API keys on a public GitHub repository. Organizations that proactively undertake these technologies shall be higher ready to guard sensitive information in an more and more complex digital landscape.
The breach was partially as a outcome of weak cryptographic practices, together with the failure to encrypt sensitive knowledge. This incident highlighted the risks of relying on outdated cryptographic methods in a high-stakes environment. Complementing these efforts, a data security marketing consultant focuses on defending delicate data by way of information governance, encryption insurance policies, Data Loss Prevention (DLP), entry controls, and regulatory compliance. Together, a cybersecurity marketing consultant and knowledge safety consultant make sure that cryptographic controls protect information all through its lifecycle whereas supporting operational resilience and enterprise continuity. This case underscores the risks of counting on weak or outdated encryption strategies for delicate information. Enterprise leaders should make sure that their organisations employ sturdy password hashing algorithms, such as bcrypt or Argon2, and implement regular updates to cryptographic protocols.